


How IAM Supports a Zero Trust Security Model
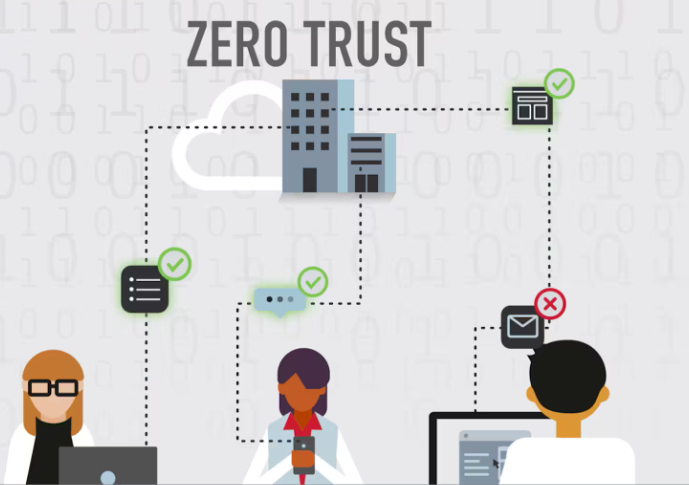
Connecting to the office network does not establish that an account should see every internal system. The device may be compromised, the employee may have changed responsibilities, or the requested resource may have nothing to do with their work. Network location provides context, but it cannot answer the whole access question. Zero trust shifts attention toward the resource and the conditions under which access is allowed. NIST describes an approach that avoids granting implicit trust solely because of location or ownership. Identity and access management supplies several necessary controls, although it cannot provide the complete architecture on its own.
Know Which Identity Is Requesting Access
Maintain dependable identity records for employees, external collaborators, and workloads. Each identity should have an accountable owner or source and an understood purpose. Unknown shared accounts make it difficult to assess a request or investigate activity later because the responsible person or process is unclear. When evaluating the best identity and access management tools, check how they connect identity records to applications and resources. A large directory is not enough. Administrators need to understand which account represents the requester, how that account was established, and whether its current status still permits the requested business relationship.
Authenticate Through an Appropriate Method
Choose authentication methods suitable for the sensitivity of the access. Protect enrollment and recovery as well as routine sign in. Strong authentication becomes less dependable when an undocumented help desk exception or alternative login route allows the same resource to be reached through weaker checks. Test the applications that matter, including older services and administrative consoles. Identify where the intended policy is enforced and where coverage differs. A central setting should be verified against actual login behavior so the team can distinguish an implemented control from a configuration that only affects part of the environment.
Make Authorization Specific to the Resource
Determine which actions the identity needs on the requested resource. Reading a document, changing its permissions, and exporting a complete dataset involve different authority. Use the available application controls to express that distinction rather than granting a broad internal user role without examining its consequences. Include conditions where they are meaningful and supported. A sensitive operation may require an approved device or a stronger authentication step. The rule should have a clear purpose and a tested outcome. Adding conditions that nobody maintains can make access unpredictable without providing reliable protection.
Use Device and Session Information Carefully
Identity is one part of the decision. Device posture, application sensitivity, and session information can also affect whether access should continue or require another check. Determine which signals are available, how current they are, and what happens when the information cannot be obtained. Avoid promising that every product reevaluates every action continuously. Enforcement differs across applications and protocols. Test the situations your policy depends on, such as a device losing an approved status or an account being disabled, and document how quickly the relevant resource responds under supported conditions.
Reduce Unnecessary Standing Access
Review permissions that remain permanently available even though they support infrequent tasks. Temporary elevation or narrowly scoped access can reduce the authority exposed during ordinary activity. Keep an approved route for additional access so employees can complete legitimate work without sharing accounts or using informal workarounds. Track role changes and departures promptly. An accurately authenticated former employee should still be denied business access once the relationship ends. Lifecycle controls connect the access decision to current organizational facts, preventing a technically valid identity from retaining permissions that no longer have a legitimate purpose.
Connect IAM With the Wider Environment
Compare identity and access management iam platforms in the context of endpoint security, application controls, network architecture, and monitoring. Ask where each access decision is made and which component enforces it. The relationships matter more than whether every vendor uses the same zero trust terminology in its product description. Start with one particularly important resource and trace the complete request path. Identify alternate routes, service identities, and emergency procedures. This exercise often reveals controls that sit outside the identity platform, such as an application's local permissions or a workload's direct connection to a database.
Expand Through Measured Changes
Pilot changes with representative users and tasks. Check both approved access and deliberate denials, then review support issues before expanding. Keep recovery and emergency access controlled so an identity service problem does not leave administrators without a legitimate way to maintain essential systems. IAM supports zero trust when identities are dependable, authentication is appropriate, permissions are specific, and changes can be enforced at the resource. The practical objective is an access decision that reflects current evidence and business need. Progress comes from understanding and improving those decisions across real systems, rather than treating a product purchase as a completed security model.

 English
 Romaian
 Greek